Homelab

A lab for the parts of IT that are hard to practice

A virtualized lab on Proxmox VE and Ubuntu Server for testing infrastructure designs: Linux administration, network segmentation, and firewall policy, kept separate from production systems.

Focus

What it's for

  • Virtualization

    Proxmox VE

    Virtual machines and containers for services and for the occasional rebuild, so breaking something costs an afternoon instead of a semester.

  • Segmentation

    Separate network paths

    Services, management, and client devices kept apart, with firewall rules deciding what may cross between them.

  • Remote access

    WireGuard tunnel

    Encrypted VPN access into the lab, scoped to the hosts and ports that actually need to be reachable.

  • Name resolution

    Pi-hole DNS

    A DNS sinkhole filtering telemetry for the whole network, plus local DNS records for internal services.

Stack

What's running

  • Proxmox VE Hypervisor
    Runs the virtual machines and containers behind the lab.
  • Ubuntu Server Guest OS
    Primary Linux environment for administration practice and services.
  • WireGuard VPN
    Encrypted tunnel for remote access from outside the network.
  • Pi-hole DNS
    Network-wide sinkhole, local DNS resolution, and query visibility.
  • UFW Host firewall
    Per-host firewall policy on the Linux guests.
  • VLAN segmentation Network
    Isolated segments for services, management, and client traffic.

Principles

How it's built

Rebuildable, not precious

Anything worth running is documented well enough to rebuild from notes instead of memory.

Segment by default

Management, services, and client devices stay on separate segments, with explicit rules between them.

Test the change twice

Firewall and DNS changes get exercised in the lab before they touch anything that matters.

Network design
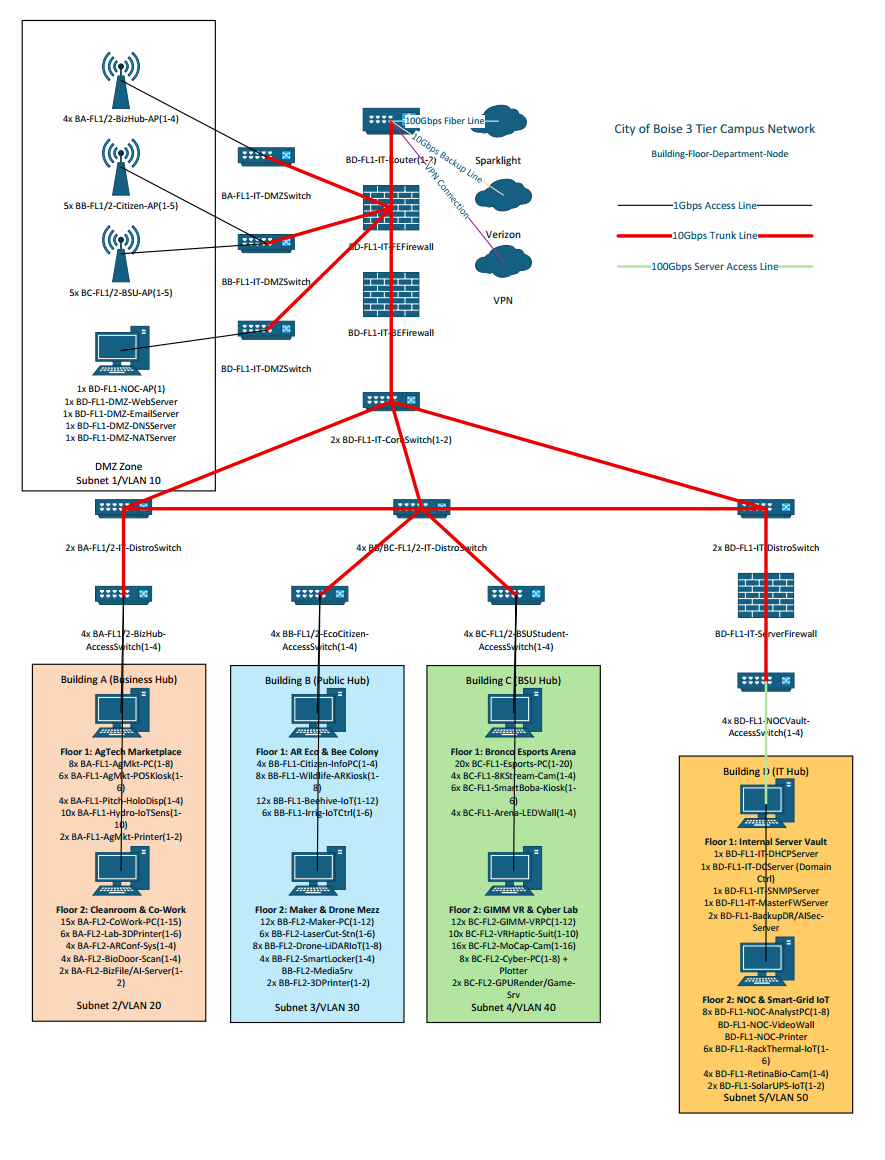
Campus network, City of Boise

Three-tier campus network diagram: two core switches, four distribution switches serving Buildings A through D, a DMZ behind paired firewalls, and redundant Sparklight and Verizon WAN links.
ITM 305 group project. Core, distribution, and access layers across four campus hubs, drawn as a Building-Floor-Department-Node plan.
  • Four hubs on their own subnets, VLAN 20 through VLAN 50
  • DMZ on VLAN 10 behind a pair of firewalls
  • 10 Gbps distribution trunks, 100 Gbps fiber to the server access switch
  • Redundant Sparklight and Verizon WAN links